Access in real time. Permissions follow the organisation.
ACCOA NeXt manages access points, credentials and permissions across sites and tenants — multi-tenant, GDPR- and NIS2-compliant, with an autonomous field level.
One system for field level, rules and evidence
From the card read at the door controller to the audit report — every step runs in the same application, without switching systems.
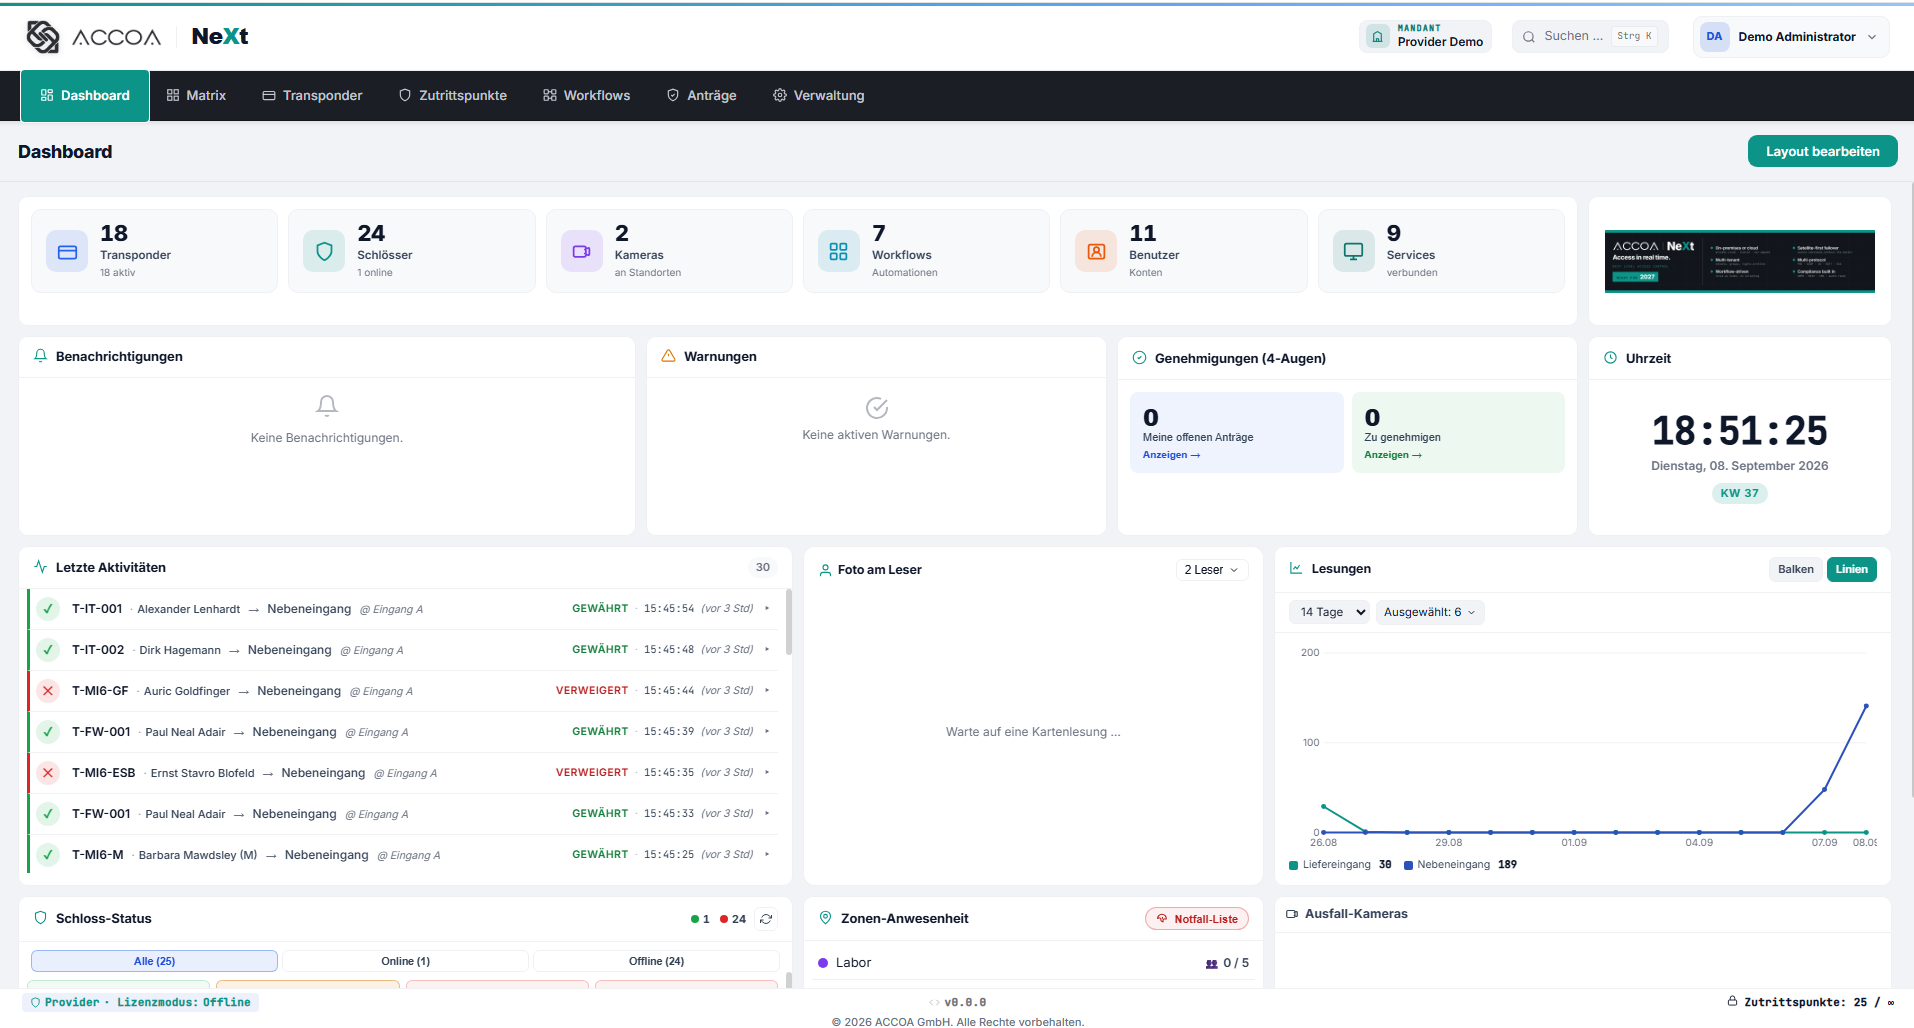
Access rules as nodes, not scripts
Triggers, conditions and actions are wired up in the editor. Every branch can be traced on its own — from the card read through time windows and dual-control approval to switching a door opener, a lamp or a push message. Changes take effect without restarting the system.
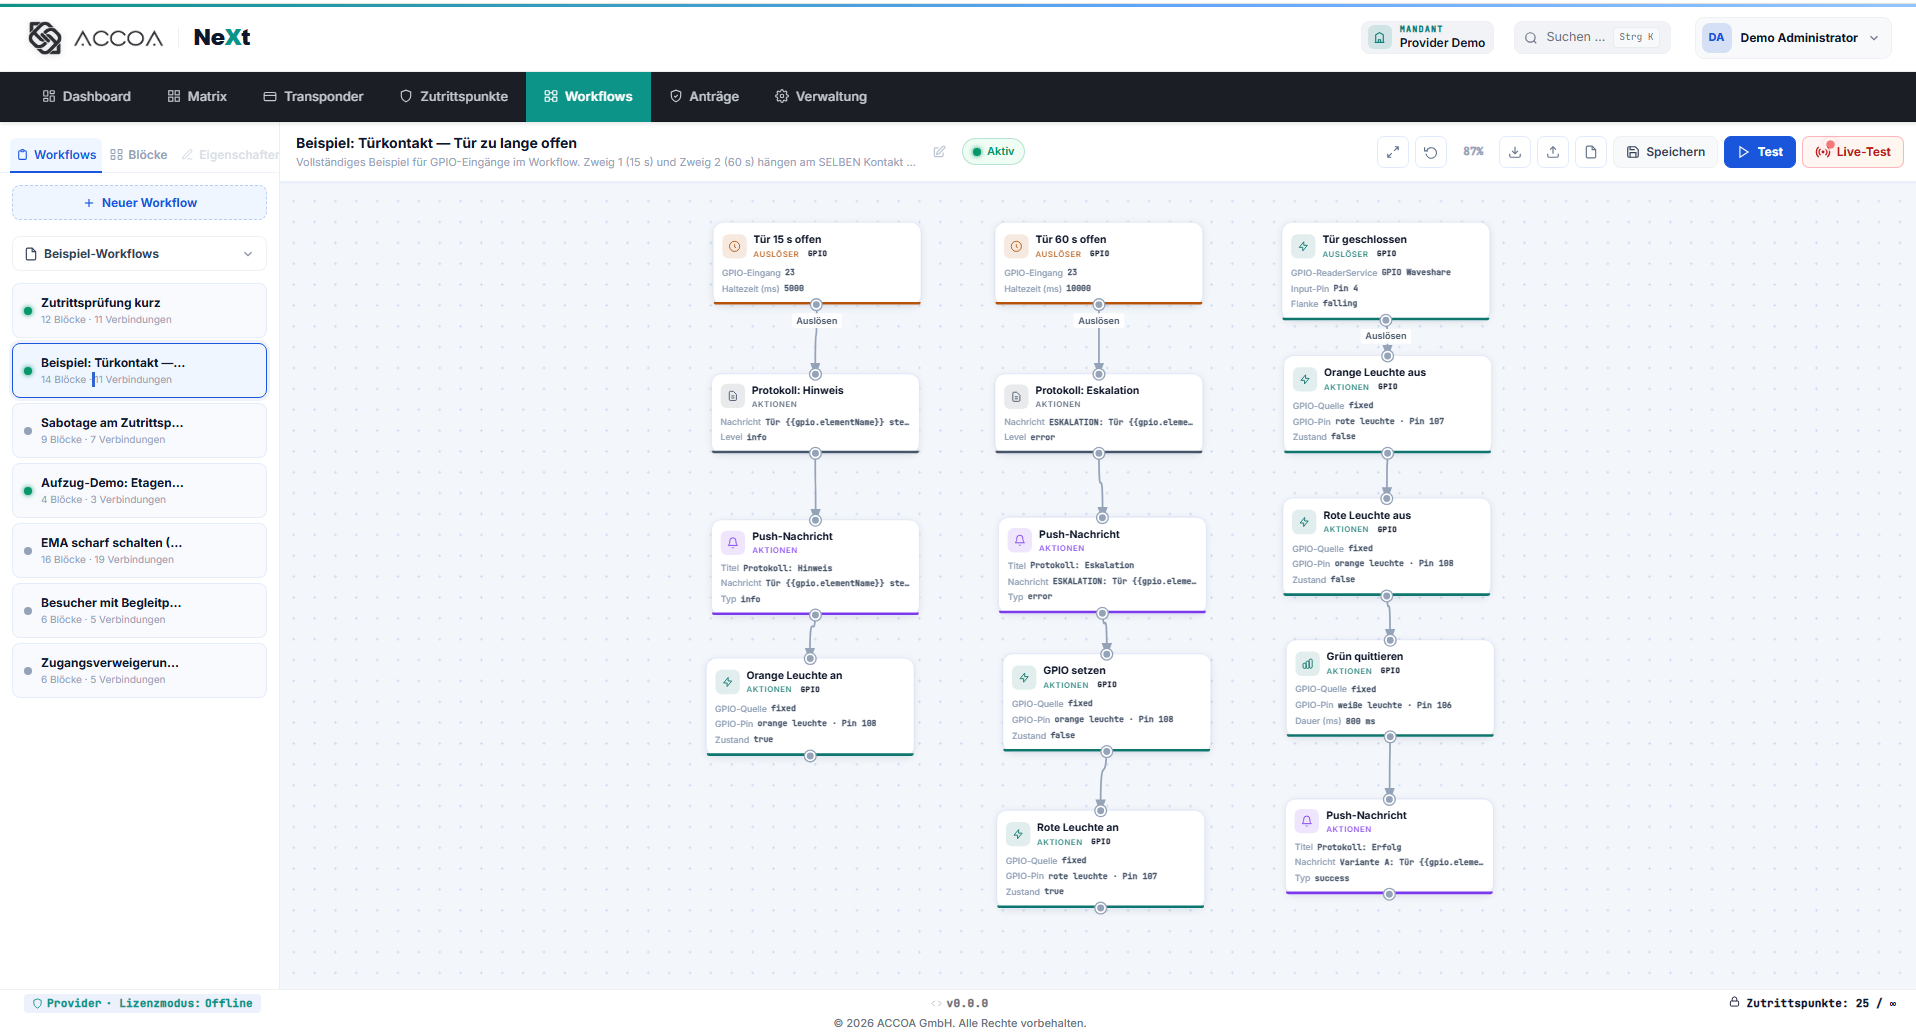
Who goes where — at a glance
Access points in the rows, credentials in the columns. The origin of every permission stays visible: set directly, inherited from a group or granted via a profile. Time windows and blocks sit alongside, and special rights such as the fire brigade run as their own column.
For properties that cannot afford downtime
The field level keeps deciding locally, even when the link to the master is down. Updates are rolled out from your own registry onto the inactive partition.
On-premises in your own data centre or as a managed installation. Containers from the local registry, no cloud requirement.
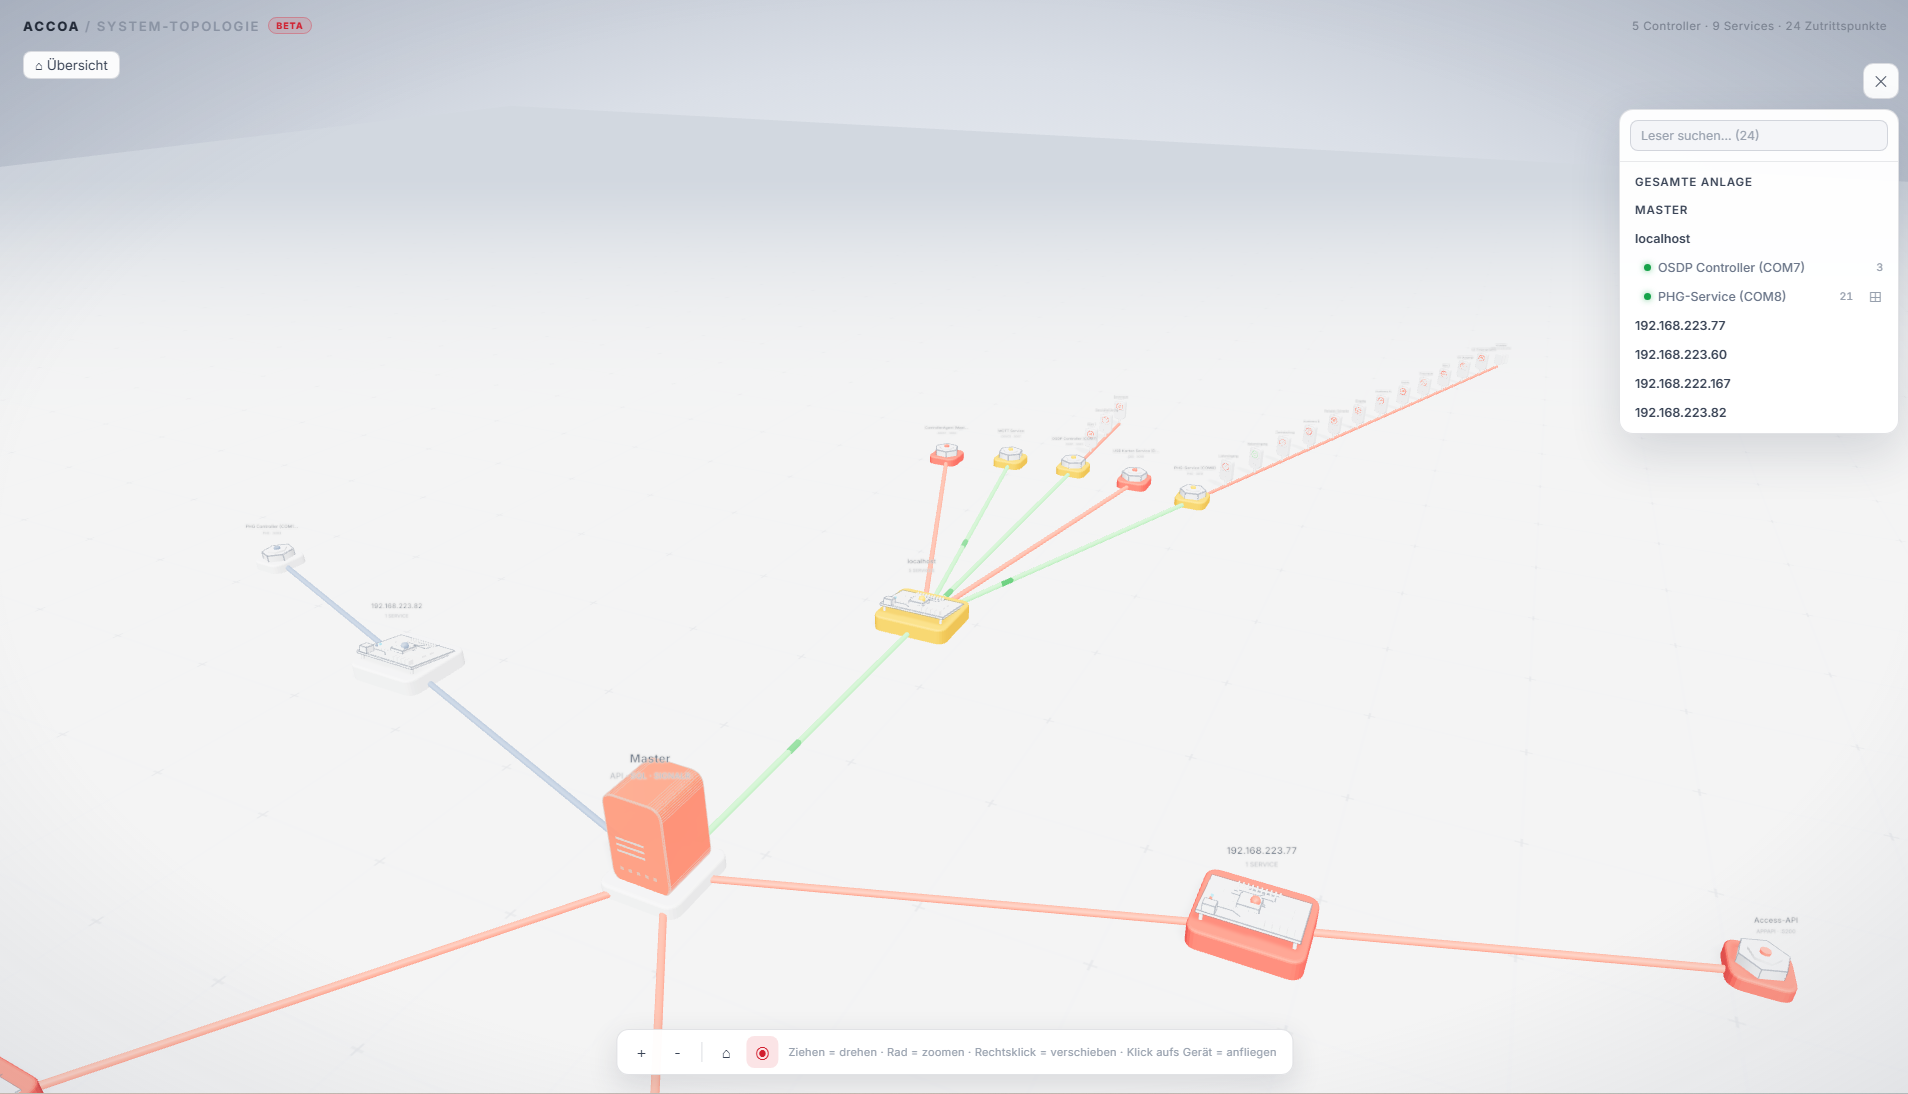
The entire system in one view
Master, controllers, services and access points shown in space, connected along the buses they sit on. The colour of each link shows its state: reachable, degraded or offline. Rotate, zoom, pan — a click on a device flies to it and opens its data.
Evidence comes from operation, not from a slide deck
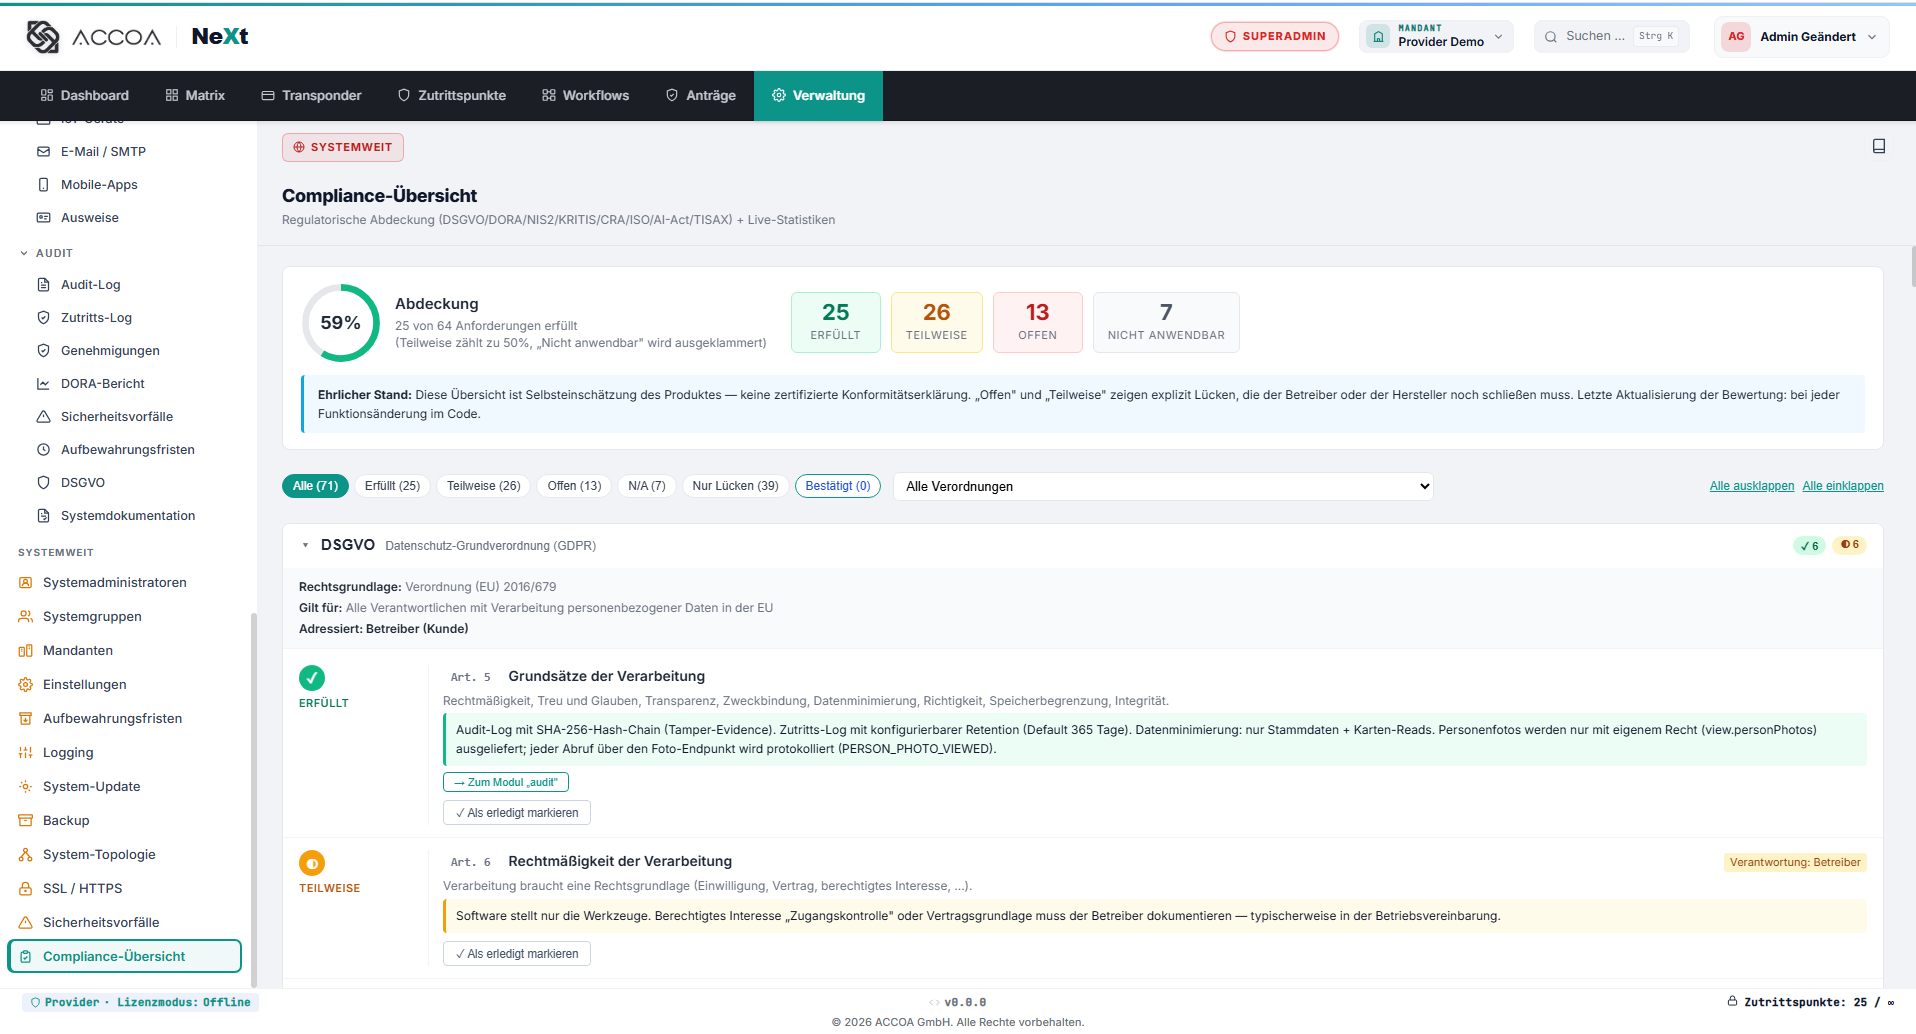
The compliance overview lists every requirement individually — with its legal basis, an assessment and a note on what the software delivers and what the operator has to document. Met, partly met and open are visibly separated and can be filtered by regulation and by gaps.
Let us talk about your property
We demonstrate the application on real readers and controllers — on site or as an online session.
63128 Dietzenbach
By sending this form you agree to your details being processed to handle the enquiry. Further information under the privacy policy.